Microsoft Security

Most organisations are paying for security capability they have never switched on.

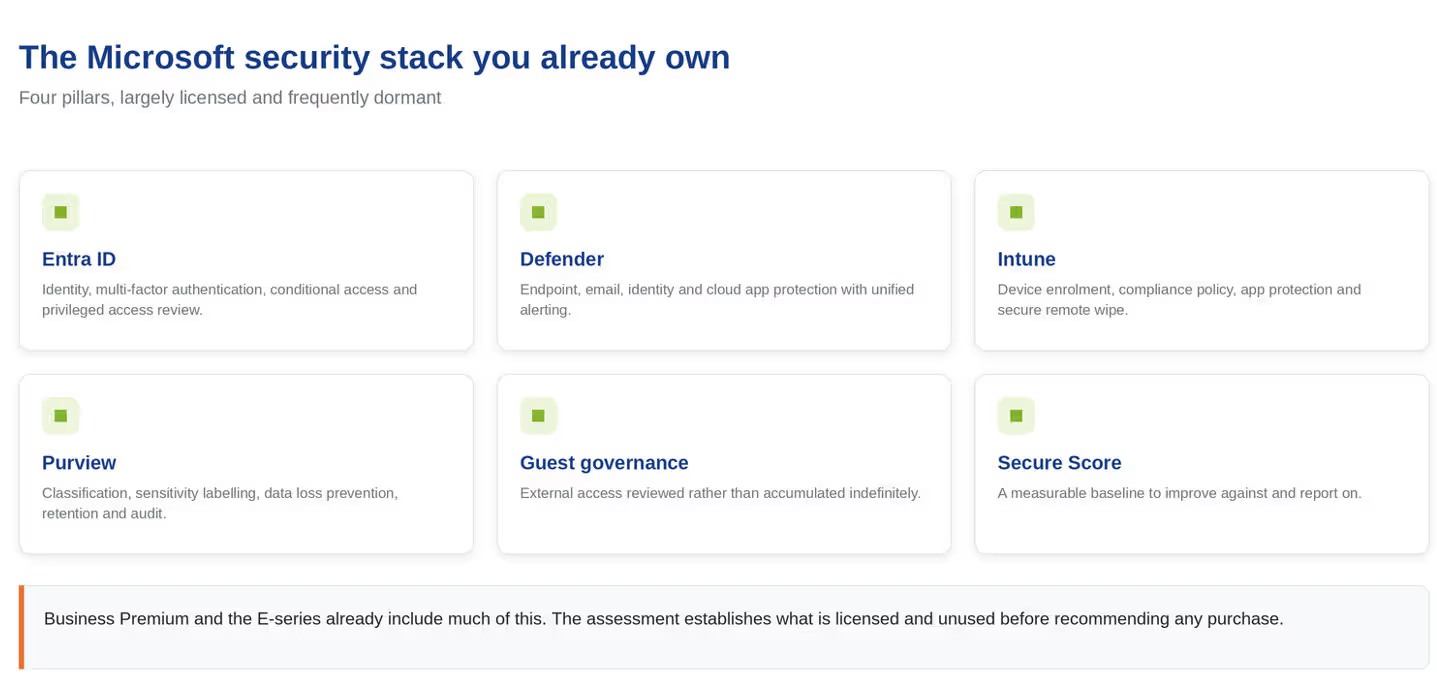
Microsoft 365 Business Premium and the E-series plans include a substantial security stack — identity protection, endpoint management, threat detection, data classification and retention. In our experience a large share of it is licensed and dormant.

That gap is where most incidents occur. Not through a sophisticated attack, but through a compromised password on an account without multi-factor authentication, or a departing employee downloading a customer list from an unmanaged laptop.

The four pillars we work across

01

Microsoft Entra ID — identity, multi-factor authentication, conditional access, privileged access review and guest governance.

02

Microsoft Defender — endpoint, email, identity and cloud app protection with unified alerting.

03

Microsoft Intune — device enrolment, compliance policy, application protection and secure remote wipe.

04

Microsoft Purview — data classification, sensitivity labelling, data loss prevention, retention and audit.
The four pillars we work across

01

Microsoft Entra ID — identity, multi-factor authentication, conditional access, privileged access review and guest governance.

02

Microsoft Defender — endpoint, email, identity and cloud app protection with unified alerting.

03

Microsoft Intune — device enrolment, compliance policy, application protection and secure remote wipe.

04

Microsoft Purview — data classification, sensitivity labelling, data loss prevention, retention and audit.

MICROSOFT SECURITY

Microsoft Security for Dynamics 365

Dynamics 365 security is not a separate problem from Microsoft 365 security. Users sign in through Entra ID, work from managed or unmanaged devices, and are subject to the same data policies as the rest of the tenant. A Dynamics 365 environment is only as well protected as the controls around it, and the four pillars above are those controls.

01

Entra ID

Multi-factor authentication and conditional access on Dynamics 365 sign-in, with regular review of administrator and privileged roles.

02

Dynamics 365 Security Roles

Least-privilege access reviewed alongside identity, with field-level protection for sensitive data such as pricing, credit limits and personal details.

03

Defender

Monitoring for risky sign-ins and unusual activity against your Dynamics 365 applications.

04

Intune

Access to Dynamics 365 limited to compliant, managed devices.

05

Purview

Audit of who viewed or changed records, and data loss prevention policies governing how Dynamics 365 data can move into other systems.

These Dynamics 365 security solutions are largely a matter of configuring products you already license, which is why the assessment starts with what you own.

Why this is now urgent

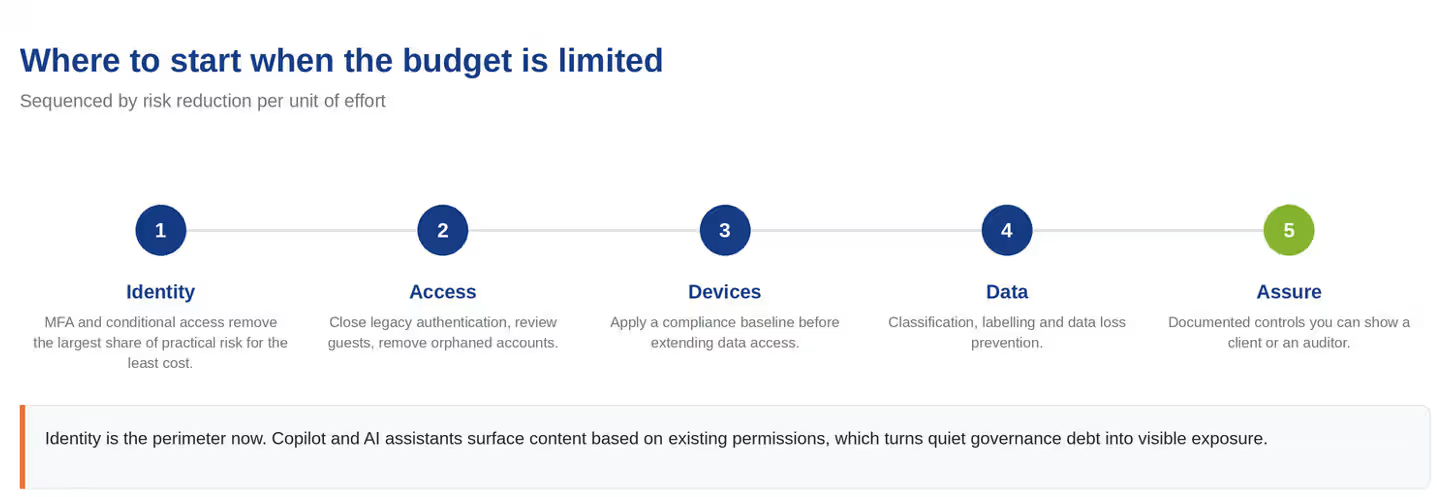
Two things changed. First, hybrid and mobile working made the network perimeter largely notional; identity is the perimeter now. Second, Copilot and AI assistants surface content based on existing permissions, which converts quiet governance debt into visible exposure.

There is also a compliance dimension. Organisations handling personal data in the UAE operate under Federal Decree-Law 45 of 2021 on personal data protection, and those in the DIFC or ADGM under their own regimes. Demonstrating control over who can access what is increasingly a contractual requirement in this market, not just good practice.

How we engage

We begin with a security assessment against the Microsoft Secure Score and your own risk profile, and produce a prioritised remediation plan. The early items are usually inexpensive and high impact: enforce multi-factor authentication, close legacy authentication, review guest access, apply a device compliance baseline.

From there we work through classification, data loss prevention and retention, which take longer because they require decisions from the business rather than configuration alone.
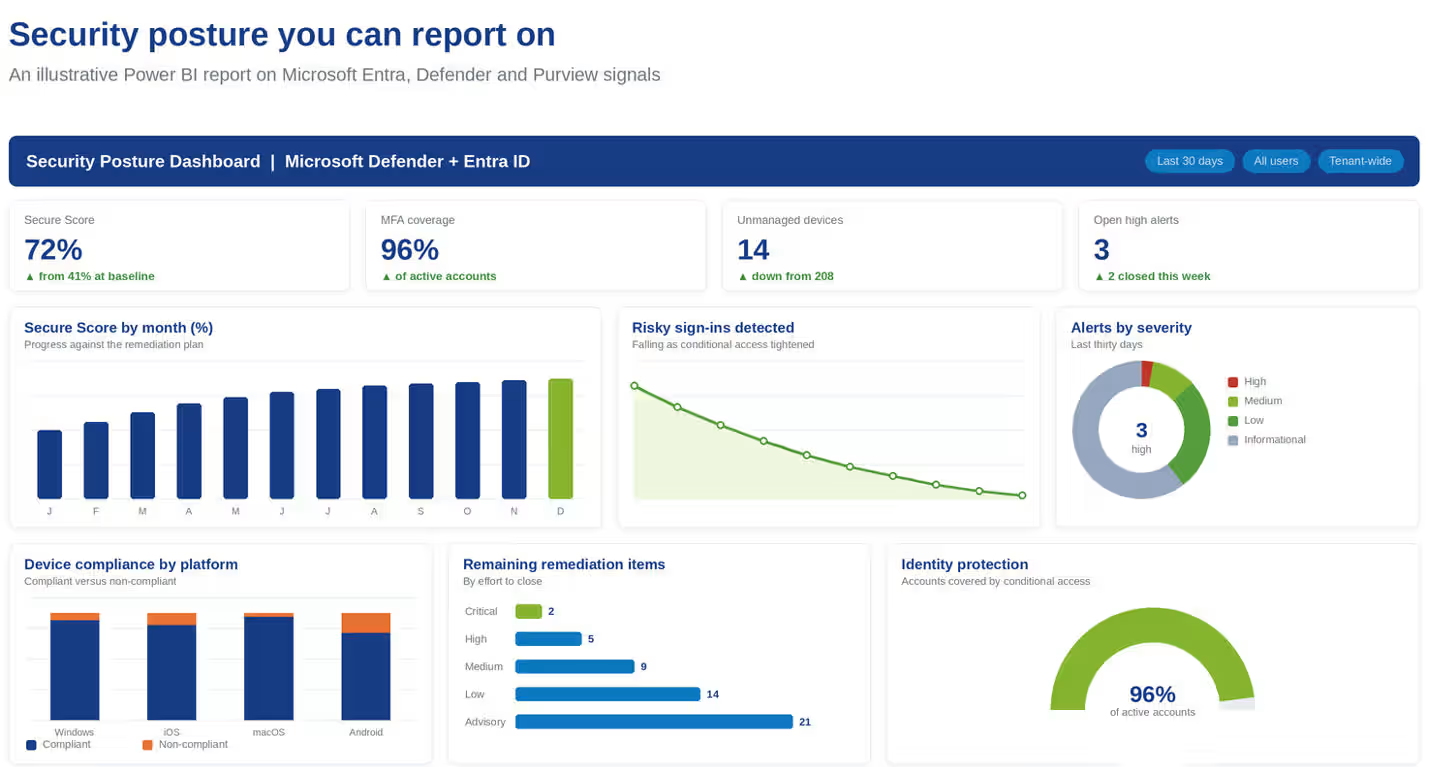
Illustrative security posture report on Entra, Defender and Purview signals

Why Dynamics Center

01

We assess what you already own before proposing anything additional.

02

We sequence remediation by risk reduction per unit of effort, so the early wins are genuine.

03

We document the control environment in a form you can show a client or an auditor.

04

Support coverage Monday to Friday, 08:00 to 18:00 Gulf Standard Time.

Frequently Asked Questions

What does Microsoft Dynamics 365 security involve?

It covers who can sign in, from which devices, what they can see and change once inside, and how activity is audited. We apply Entra ID, Intune, Defender and Purview controls around your Dynamics 365 environment and review its own security roles alongside them.

Do we need additional licences?

Frequently not. Business Premium and the E-series already include much of this. The assessment establishes what is licensed and unused before recommending any purchase.

How long does an assessment take?

Typically one to two weeks, producing a prioritised remediation plan with effort and impact against each item.

Can you help with UAE PDPL compliance?

We can implement the technical controls — classification, retention, access governance and audit. Legal interpretation of your obligations should come from your legal advisers; we work alongside them.

Do you provide ongoing monitoring?

Yes, under a managed services agreement, including alert triage and periodic posture review.

Where do we start if the budget is limited?

Identity. Multi-factor authentication and conditional access remove the largest share of practical risk for the least cost.

Dynamics Center

Book a security posture assessment

Speak to a certified Microsoft partner based in Business Bay, Dubai.

Contact Dynamics Center

Landline +971 4 254 0212
Mobile +971 55 625 5794

info@dynamicscenter.com

2405 Clover Bay Tower, Business Bay, Dubai, United Arab Emirates

Coverage hours: Monday to Friday, 08:00 to 18:00 Gulf Standard Time.

×

    Get in Touch for Pricing

    LinkedIn WhatsApp Chat info@dynamicscenter.com
    ×